|
|
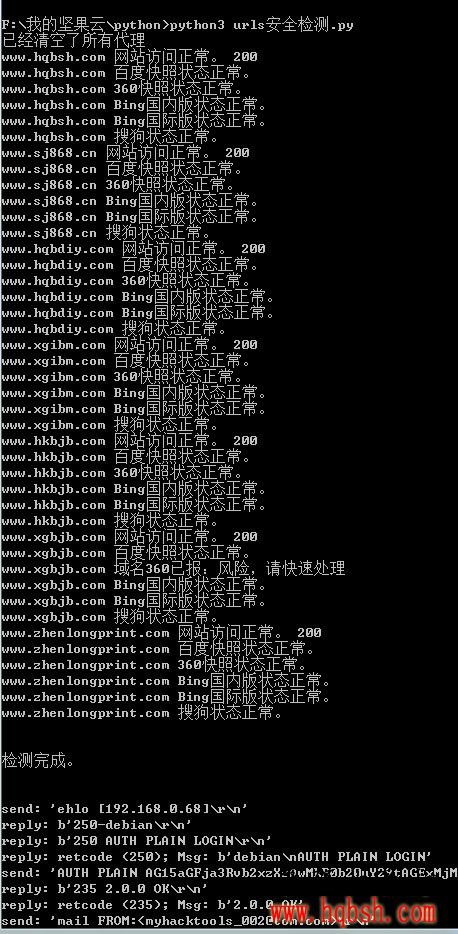
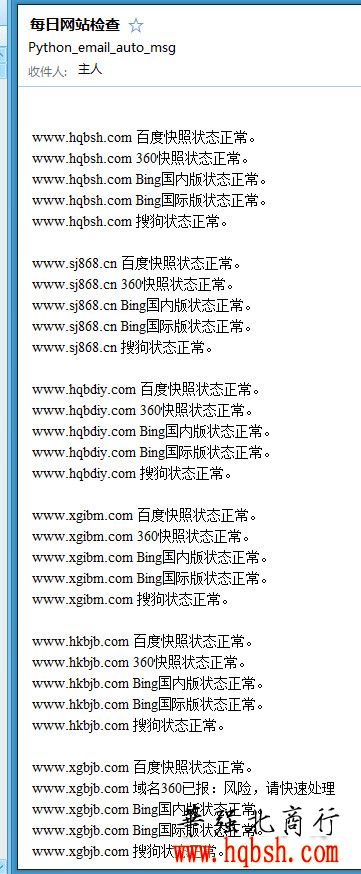
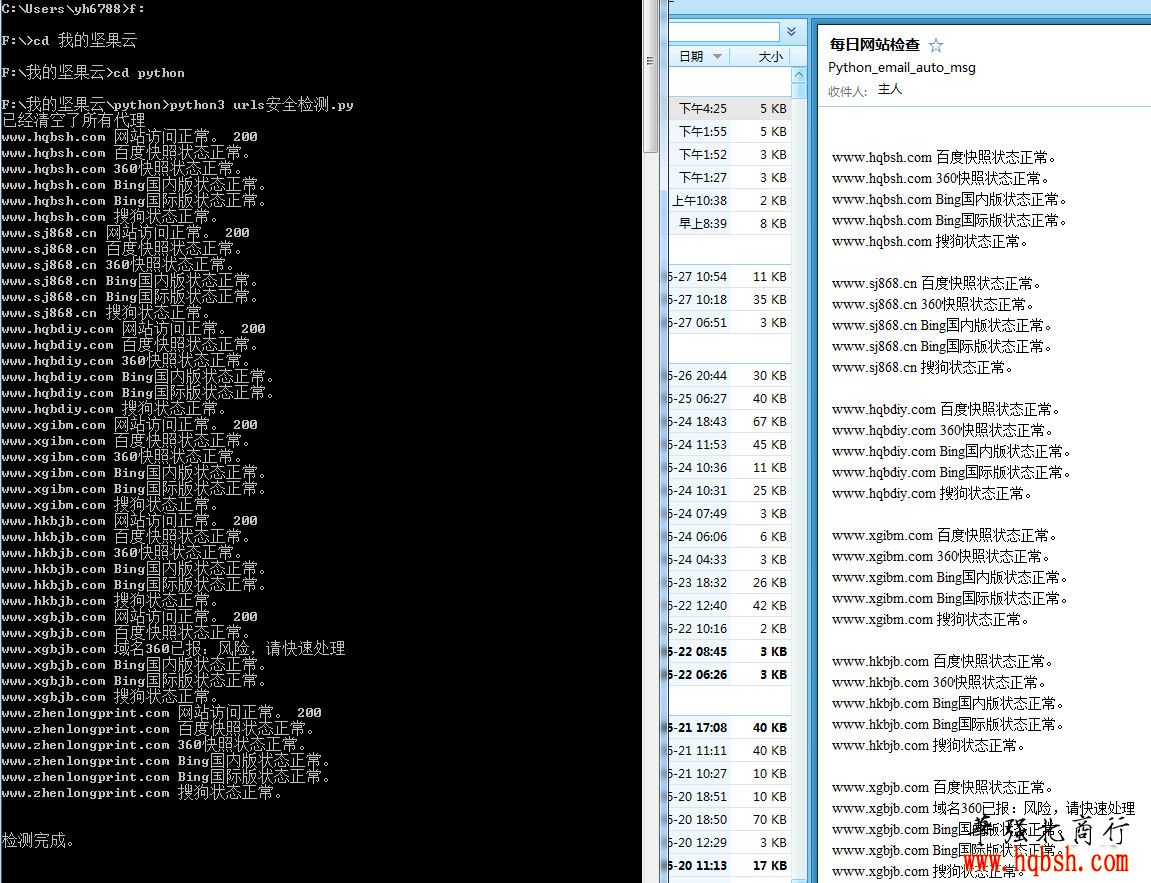
自动检测网站有没有被入侵,百度,360,sogou,bing收录是否正常,并发邮件给指定帐户
- import requests
- import yh_dl,time,os
- import yh_email
- def save(html):
- name="1.html"
- html1=html.content
- with open(name,"wb") as f:
- f.write(html1)
- def baidu_test(i,headers,txt_mail):
- #循环读取所有所有域名进行凭拼接
- baidu_domain = "https://www.baidu.com/s?ie=UTF-8&wd=site%3A"+i
- #指定访问all_urls中的所有域名
- html = requests.get(baidu_domain,headers=headers).text
- if "风险" in html:
- txt=i+' 域名百度已报:风险,请快速处理'
- else:
- txt=i+' 百度快照状态正常。'
- print(txt)
- txt_mail=txt_mail+txt+'\n'
- return txt_mail
- def test_360(i,headers,txt_mail):
- html_360='https://www.so.com/s?q=site%3A'+i+'&src=srp&fr=none'
- html = requests.get(html_360,headers=headers)
- html_1=html.text
- if "虚假" in html_1:
- # print(html_1)
- save(html)
- # os.exit
- txt=i+' 域名360已报:风险,请快速处理'
- else:
- txt=i+' 360快照状态正常。'
- print(txt)
- txt_mail=txt_mail+txt+'\n'
- return txt_mail
- def test_bing(i,headers,txt_mail):
- for ii in (0,1):
- if ii==0:
- txt1='Bing国内版'
- else:
- txt1='Bing国际版'
- html_url='https://cn.bing.com/search?q=site%3A'+i+'&FORM=BESBTB&ensearch='+str(ii)
- html = requests.get(html_url,headers=headers)
- html_1=html.text
- if "风险" in html_1:
- # print(html_1)
- save(html)
- # os.exit
- txt=i+' 域名%s已报:风险,请快速处理'%txt1
- else:
- txt=i+' %s状态正常。'%txt1
- print(txt)
- txt_mail=txt_mail+txt+'\n'
- return txt_mail
- def test_sogou(i,headers,txt_mail):
- txt1='搜狗'
- headers={
- 'Accept': 'text/html,application/xhtml+xml,application/xml;q=0.9,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9',
- 'Accept-Encoding': 'gzip, deflate, br',
- 'Accept-Language': 'zh,zh-CN;q=0.9',
- 'Connection': 'keep-alive',
- 'Cookie': 'CXID=716ABD167F96C2985337CB890C9E7462; ad=gkllllllll2Wdk$alllllVELjo7lllllVGwlLlllll9lllllpOxlw@@@@@@@@@@@; SUID=D800C2141824A00A5EF60A8B00048552; ABTEST=1|1593237758|v17; SUV=1593237750045371; browerV=3; osV=1; sct=1; SNUID=A0779B96E1E548EB72E449DFE19BDB78; sst0=768; taspeed=taspeedexist; pgv_pvi=3457337344; pgv_si=s3333383168; IPLOC=KR; ld=pkllllllll2Wdm99lllllVELiallllllNTmQyyllll6lllllpZlll5@@@@@@@@@@; LSTMV=718%2C24; LCLKINT=180423',
- 'Host': 'www.sogou.com',
- 'Referer': 'https://www.sogou.com/web?query=site%3Awww.hqbsh.com&_asf=www.sogou.com&_ast=&w=01019900&p=40040100&ie=utf8&from=index-nologin&s_from=index&sut=3818&sst0=1593237755768&lkt=18%2C1593237751951%2C1593237755510&sugsuv=1593237750045371&sugtime=1593237755768',
- 'Sec-Fetch-Dest': 'document',
- 'Sec-Fetch-Mode': 'navigate',
- 'Sec-Fetch-Site': 'same-origin',
- 'Sec-Fetch-User': '?1',
- 'Upgrade-Insecure-Requests':'1',
- 'User-Agent': 'Mozilla/5.0 (Windows NT 6.1; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/83.0.4103.116 Safari/537.36',
- }
- t=str(int(time.time()*1000))
- html_url='https://www.sogou.com/web?query=site%3A'+i
- # html_url='https://www.sogou.com/web?query=site%3A'+i+'&_ast='+t+'&_asf=www.sogou.com&w=01029901&p=40040100&dp=1&cid=&s_from=result_up'
- html = requests.get(html_url,headers=headers)
- html_1=html.text
- if "安全风险" in html_1:
- print(html_1)
- save(html)
- # os.exit
- txt=i+' 域名%s已报:风险,请快速处理'%txt1
- else:
- txt=i+' %s状态正常。'%txt1
- print(txt)
- txt_mail=txt_mail+txt
- return txt_mail
- def main():
- # 列出所有查询的网址域名
- all_urls =[
- "www.hqbsh.com",
- "www.sj868.cn",
- 'www.hqbdiy.com',
- 'www.xgibm.com',
- 'www.hkbjb.com',
- 'www.xgbjb.com',
- 'www.zhenlongprint.com',
- ]
- user_agent="Mozilla/5.0 (Windows NT 6.1; WOW64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/44.0.2403.157 Safari/537.36"
- headers={"User-Agent":user_agent}
- # headers={
- # "Referer":'www.baidu.com',
- # "User-Agent":"Mozilla/5.0 (Windows NT 6.1; WOW64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/44.0.2403.157 Safari/537.36",
- # "Accept-Encoding":"gzip, deflate",
- # "Accept-Language":"zh-CN,zh;q=0.8",
- # "Connection":"keep-alive"
- # }
- txt_mail=''
- for i in all_urls:
- print('\n')
- txt_mail=txt_mail+'\n'
- domain = "http://" + i
- try:
- code = requests.get(domain)
- txt_temp=i+' 网站访问正常。 '+str(code.status_code)
- txt_mail=txt_mail+'\n'
- print(txt_temp)
- except:
- #调试异常情况
- txt_temp=i+ " 域名出现无法访问问题,请及时排查问题"
- #跳出当前循环
- print(txt_temp)
- txt_mail=txt_mail+'\n'
- continue
- else:
- if code.status_code == 200:
- #循环读取每一个网站的情况
- html = code.text
- if "<script>document.title=" in html:
- print("您的网站:",i,"已出现疑似入侵信息,请快速处理")
- txt_mail=txt_mail+"您的网站:"+i+"已出现疑似入侵信息,请快速处理"+'\n'
- txt_mail=baidu_test(i,headers,txt_mail)
- txt_mail=test_360(i,headers,txt_mail)
- txt_mail=test_bing(i,headers,txt_mail)
- txt_mail=test_sogou(i,headers,txt_mail)
- print("\n\n检测完成。\n\n")
- txt_mail=txt_mail+'\n\n检测完成\n'
- yh_email.email_txt(txt_mail,'每日网站检查')
- os.system('pause')
- yh_dl.kill_system_dl()
- main()
|
-
|


 发表于


 发表于